
Source? The closest I found was microsoft's key escrow system, but that's hardly a "backdoor" given it's publicly documented, and it's explicitly stated in no uncertain terms when you're setting it up[1]
[1] https://static0.howtogeekimages.com/wordpress/wp-content/upl...
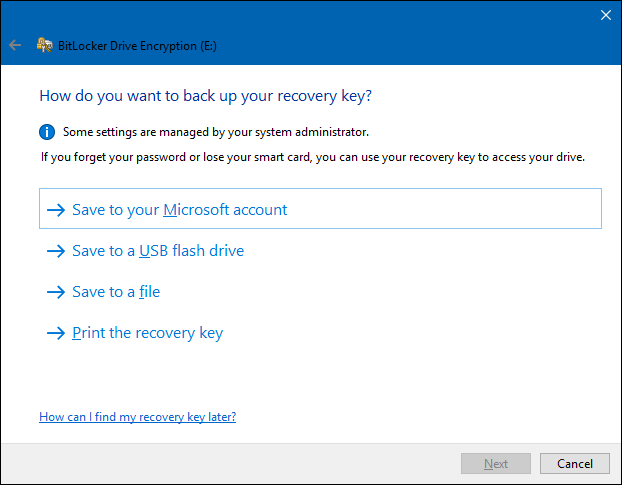
I'm not 100% certain either way.
What Bitlocker/TPM did accomplish was booby-trapping peoples PC. You are met with the recovery blue-screen if you went through the effort of installing an offline account, and tried to dual boot off the same physical drive. No one is told to backup your recovery key post install, and so the incentive to always use their shitty cloud options is encouraged with data loss.
Note too, NTFS will have encryption auto-enabled on anything you plug into Windows 11. Note, post-install it is non-trivial to fix the troublesome behavior.
Rufus is now the only way to install Windows 11 pro without the enshittification features:
https://github.com/pbatard/rufus/releases
Ripping out all the "AI" (undocumented API areas indicate snitch-ware), spam, and telemetry nonsense takes some effort. However, the only thing that should be running on windows now is the Steam launcher for classic games, and a tool to neuter most of the Microsoft malware.
https://www.oo-software.com/en/shutup10
It is sad, but Microsoft has some people willing to burn company goodwill for short-term gains. Even xbox now sucks, and that was easy money. =3